· cyber security · 4 min read
Before Your Front Desk Pastes Patient Notes Into ChatGPT
Nobody at your practice is trying to leak patient data — they’re trying to clean up a note before 5 p.m. Here’s what actually leaves the building when someone pastes into a free AI tool, and what to do about it this week.
Before Your Front Desk Pastes Patient Notes Into ChatGPT
It’s 4:50 on a Thursday.
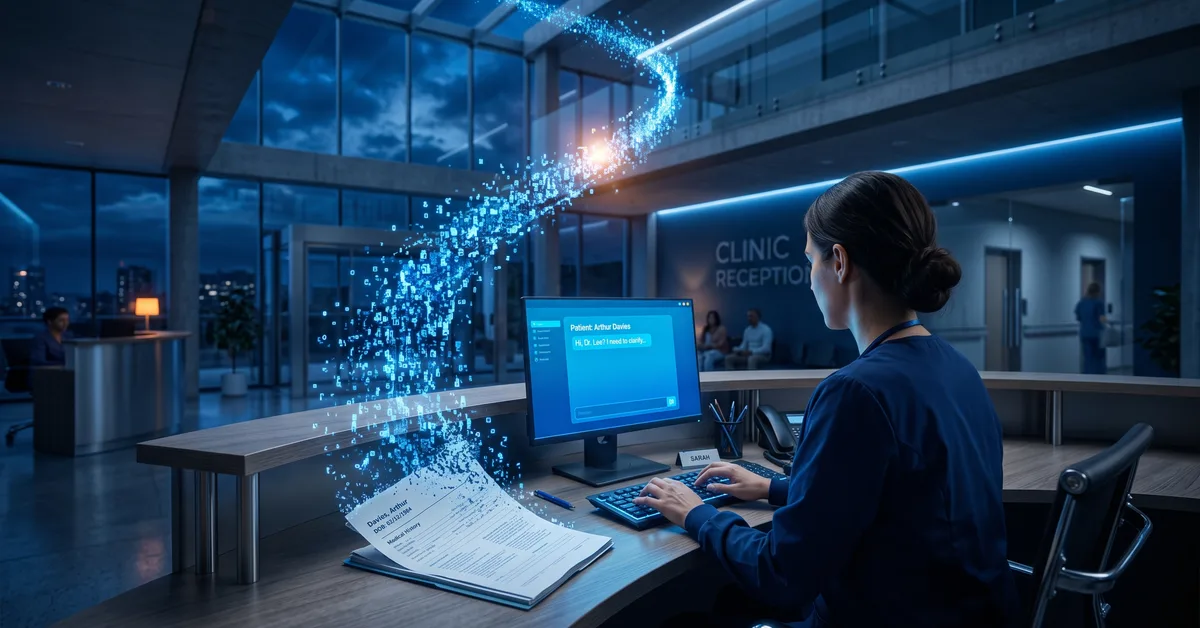
A referral letter needs to go out, the wording is awkward, and the fastest fix is to paste it into a chat window and ask for a cleaner version.
Nobody thinks of that as a data transfer. It feels like spell-check.
But the letter has a name, a date of birth, a diagnosis, and a treatment plan in it. And it just went somewhere your practice has no agreement with, no visibility into, and no way to get it back from.
This is happening in practices right now. Not because staff are careless, but because the tools are free, fast, and genuinely helpful.
Here are four things every owner-doctor should understand about it.
It has already happened in your office
If you haven’t explicitly told your team which AI tools are approved, assume they’ve picked their own.
Front desk staff use it to rewrite emails. Billing uses it to decode a denial. A hygienist uses it to explain a procedure in simpler words for a patient handout. Your associate uses it to summarize a journal article.
Every one of those is a reasonable person doing a reasonable thing. The problem is that none of them were told where the line is, so the line is wherever each of them guessed.
Ask your team this week. Not as an accusation, as an inventory. You’ll likely be surprised by how many tools are already in use.
What actually leaves when you paste
When protected health information (PHI) goes into a consumer AI tool, several things can happen at once.
The text is stored on the vendor’s servers, often for a period you don’t control. Depending on the account type, it may be used to train future models. It may be reviewed by humans for quality. It’s now subject to the vendor’s breach, not just yours.
And there’s no Business Associate Agreement (BAA) in place. That’s the contract HIPAA expects between your practice and any vendor that handles PHI on your behalf. Consumer AI tools don’t sign one. Which means from a HIPAA readiness standpoint, the data went to an unauthorized party.
A single pasted note is unlikely to make headlines. A pattern of them, discovered during a breach investigation or an audit, is a different conversation.
The free tier is the expensive one
The tools your staff are using for free are the ones with the fewest protections.
Business and enterprise tiers of the same products typically offer things the free version doesn’t: your data excluded from training, shorter retention, admin controls, and in some cases a BAA.
They cost money per user per month. That number is small compared to the cost of a reportable incident, a breach notification mailing, or a cyber insurance claim that gets questioned because the practice had no AI controls.
If your team is going to use AI (and they are), the question is whether you’d rather pay for the version that has an agreement with you or keep using the one that doesn’t.
What to do this week
You don’t need a 20-page policy to fix most of this. You need three decisions and a conversation.
Decide:
- Which one or two AI tools are approved, on which account tier
- What never gets pasted: patient names, dates of birth, chart details, images, billing records
- Who approves a new tool before anyone starts using it
Then say it out loud at the next staff meeting. Write it on one page. Put it where the hand-washing sign is.
The goal isn’t to scare people away from a useful tool. It’s to make the safe version the easy version, so the 4:50 p.m. shortcut goes through a door you chose.
The shortcut isn’t the problem. The silence is.
Your team will keep finding faster ways to do their work. That’s a good instinct and you want to keep it.
What creates the risk is a practice that never said anything, so every employee is deciding privacy policy at their own keyboard.
A short conversation and a short list changes that. A reviewed tool with a real agreement changes it further. And knowing what’s actually in use across your practice is where both of those start.
We help practices take inventory of the tools their teams are actually using, sort out which ones are safe for patient information, and put simple guardrails in place. It starts with a 10-minute discovery call.
Call us at 405-253-5101 or schedule a discovery call to get on the calendar.