· managed it · 4 min read
Where Does Your Patient Data Actually Live?
Ask your office manager where patient data is stored and count the pauses. The honest list is a lot longer than the practice-management system. Here are the places it hides — and how to build a data map in one afternoon.
Where Does Your Patient Data Actually Live?
Try this tomorrow morning.
Ask your office manager, your lead assistant, and your billing person the same question: “Where is our patient data stored?”
The first answer will be the practice-management system. That’s correct, and it’s maybe a third of the truth.
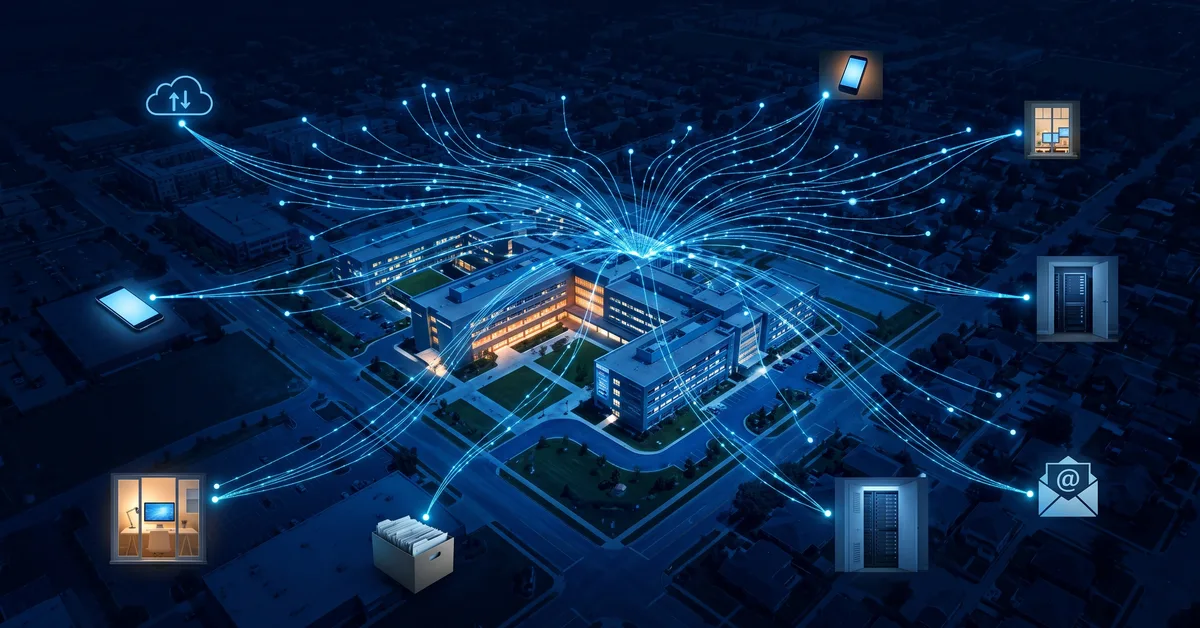
Then come the pauses. The imaging server. The email. The scanned forms in a shared drive. The texting app. The old computer in the back that was never wiped. The AI scribe. The vendor portal for the lab.
Every one of those is a place protected health information (PHI) lives. Most practices have never written the list down.
Here are five things owner-doctors should know about that list.
The list is longer than the practice-management system
Data governance sounds like a term for hospitals and banks. In a small practice, it means one thing to start: knowing where your patient information is.
Not where it’s supposed to be. Where it actually is.
You can’t protect a location you don’t know about. You can’t include it in a backup. You can’t confirm it’s encrypted. You can’t tell an auditor or an insurer that it’s covered. And you can’t answer a patient who asks what you hold about them.
The inventory is the foundation everything else sits on.
The common hiding places
Practices are consistent in where data ends up. Check these first:
- Email, especially attachments: referral letters, records requests, X-rays sent to specialists
- Imaging systems and the workstations connected to them
- Cloud drives and shared folders holding scanned intake forms, consents, and IDs
- Phones and tablets, including personal devices with practice email or the patient-texting app
- AI tools, transcription services, and any browser extension staff installed themselves
- Retired hardware: old servers, replaced laptops, external drives in a drawer
- Vendor portals: labs, payers, clearinghouses, and the marketing platform that has patient contact lists
If a location on that list surprised you, it’s not on your backup plan either.
Why you can’t protect what you haven’t mapped
Every safeguard your practice relies on assumes a known set of locations.
Encryption protects the devices you know to encrypt. Backups cover the systems you pointed them at. Access controls limit who reaches the folders you set them on. Vendor agreements cover the vendors you listed.
An unmapped location has none of that by definition. It’s not that the safeguard failed. It’s that the safeguard never knew to try.
That’s why most incidents in small practices don’t come from the main system. They come from the laptop nobody tracked, the shared folder nobody restricted, the old drive nobody wiped.
A data map in one afternoon
This doesn’t require a consultant with a whiteboard. It requires a spreadsheet and three hours.
For each place patient data lives, write down:
- What kind of data is there (records, images, contact info, billing)
- Who can access it
- Whether it’s encrypted and backed up
- Which vendor is involved, and whether there’s a signed agreement
- Whether it should still exist at all
The last column is often the most useful. A surprising amount of what turns up shouldn’t be there anymore.
Walk the building. Ask each role what they touch. Log into the cloud accounts and look. Open the drawer.
Governance starts with an inventory
The word “governance” tends to intimidate. All it means at this stage is that someone knows where the data is, someone is responsible for each place, and the list gets updated when things change.
That inventory is the first thing a risk assessment needs. It’s what makes an encryption rollout complete instead of partial. It’s what makes an AI policy enforceable, because you know which tools hold what. And it’s the document that turns a breach investigation from a scramble into a lookup.
Everything else in data governance builds on it. Nothing works without it.
We help practices build that map, find the locations they didn’t know about, and put the right protections on each one. It starts with a 10-minute discovery call.
Call us at 405-253-5101 or schedule a discovery call to get started.