· cyber security · 4 min read
MDR vs EDR: What Your Internal IT Team Actually Needs
MDR vs EDR comes down to software versus people. Here is what each one does, why a small internal IT team can run EDR but can't watch alerts all night, and how co-managed IT splits the work.
Say your contact center has 150 agents. Some sit in the office, some work from home, and a nearshore team covers late shifts in another time zone. Laptops are everywhere. Your IT team is two people who work business hours.
Someone suggests adding MDR. The IT manager hears “you’re being replaced” and the owner hears “another monthly bill.” Both reactions make sense, mostly because the acronyms are confusing. Here is how MDR vs EDR breaks down, and where each one fits when you already have in-house IT.
Antivirus, EDR, and MDR in plain words
Antivirus checks files against known bad patterns and blocks what it recognizes. It is a fine baseline. It misses attacks that use normal tools in bad ways, like a script running under a legitimate admin account.
Endpoint detection and response (EDR) is software installed on each computer and server. It records what happens on the device: programs starting, scripts running, connections opening. It flags suspicious behavior and can cut an infected machine off from the network with one click. It cannot read its own alerts.
Managed detection and response (MDR) is a service. A team of analysts watches the alerts from your EDR around the clock, decides which ones are real, and acts on them. Usually that means isolating a machine and telling you what they saw.
What a small internal team can own
Your IT manager is the right person to own the EDR deployment. They know which machines exist, which ones are missing an agent, and which business applications will trip a detection. Softphone clients, call recording tools, and older line-of-business applications (the ERP or CRM your company runs on) do this often. Someone who knows the environment has to decide whether a flagged program is normal.
That work happens during business hours, and one or two people can do it well.
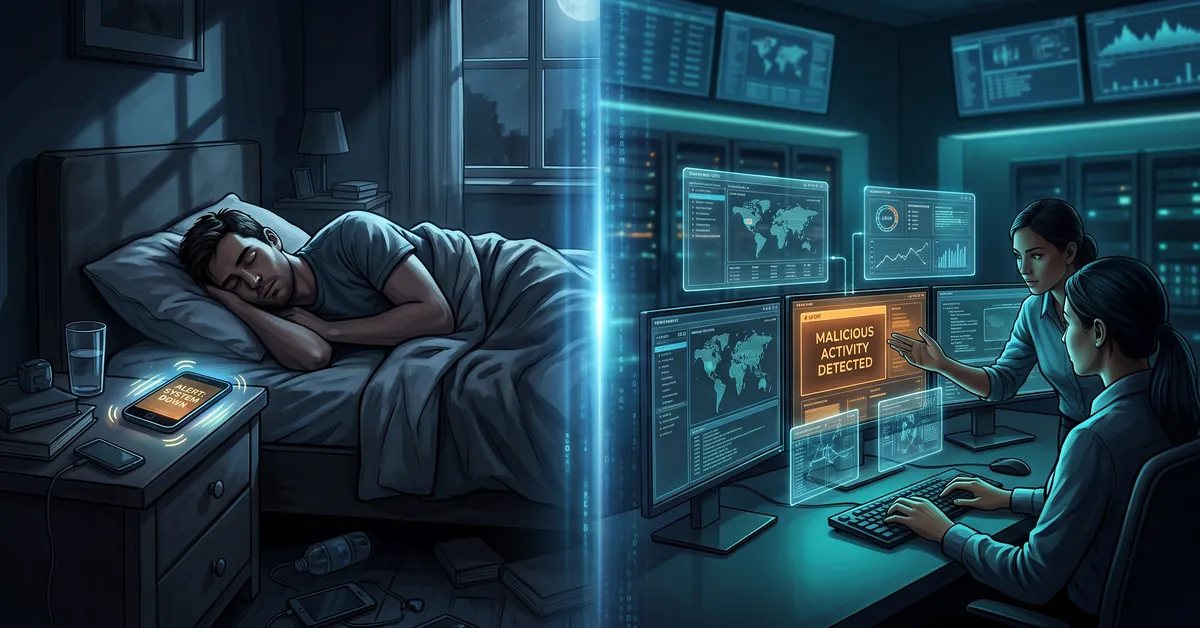
Watching the console is a different job. An alert that fires at 11 p.m. on Friday and gets read at 8 a.m. on Monday has had the whole weekend to spread. Covering 168 hours a week takes a rotation of people, and a team of two can’t staff that without burning out.
A person paged at 2 a.m. also has to tell a false alarm from a real intrusion while half asleep. That takes practice, and analysts who do it all day get plenty.
Questions to ask an MDR provider
Get plain answers to these before you sign:
- Who can isolate a machine, and do they have to call us first?
- How fast do you act, measured from the alert firing to the first containment step, and is that number in the contract?
- Can you monitor the EDR we already own, or do you require your own agent?
- What do you finish yourselves, and what do you hand back to us? Reimaging, password resets, and user interviews are common handoffs.
- Who do you call at 3 a.m., and what happens if nobody answers?
- Who tunes out false positives from our own business applications?
- Will we keep access to the console and to a written record of every action you took?
The first two answers matter most. A provider that can only send an email, at its own pace, is a notification service. You want one that can contain a problem quickly and tell you afterward, inside limits you agreed on in advance.
How co-managed IT divides the work
In co-managed IT, the internal team keeps the work that depends on knowing the place, and the MSP (managed service provider) takes the work that depends on staffing.
Your internal IT team typically owns:
- the device inventory, so every machine has an agent
- approving exceptions for software that trips detections
- user-facing recovery, like getting an agent back on a clean laptop
The MDR provider typically owns:
- 24/7 alert review
- containment actions inside the agreed limits
- investigation notes and a written report afterward
Write down which actions the provider may take without a call. Isolating a single agent’s laptop is an easy yes. Disabling a user account is probably a yes. Shutting down the server that runs your phone system or billing should wait for a person at your company to say go.
Put those limits on one page and keep a copy where the IT manager and the owner can both find it.
How Kayak Cyber helps
We work alongside in-house IT teams. We provide 24/7 managed detection and response, with people watching alerts around the clock who can isolate a device. We also correlate alerts across endpoints, email, identity, and cloud, so related signals show up as one incident. That matters for attacks that never touch a laptop, like a stolen Microsoft 365 password used from another country. Your IT manager keeps authority over the environment and gets the nights and weekends back. Read more about our cybersecurity services and our co-managed IT model.
Call us at 405-253-5101 or schedule a discovery call to get on the calendar.