Below the Rapids
An Incident Response Plan for Co-Managed Teams: Who Calls Whom
When something goes wrong, the first hour is about phone calls. This post lays out call order, decision rights, outside obligations, evidence preservation, and a sample responsibility split for co-managed IT teams.
Immutable Backups and the Restore Test Nobody Schedules
Most organizations have backups. Fewer have restored from them. This post covers 3-2-1-1-0, why attackers hit backups first, Microsoft 365 backup, and a restore testing schedule that internal IT and an MSP can share.
Conditional Access: The Microsoft 365 Settings Small IT Teams Skip
Conditional Access is already included in many Microsoft 365 plans and sits unused. These five policies, rolled out in report-only mode first, are a good starting point for co-managed IT teams.
Phishing-Resistant MFA and the Limits of Text Message Codes
Text message codes beat a password alone, but SIM swaps, push bombing, and relay phishing kits get around them. A co-managed IT team can move remote and office staff to phishing-resistant MFA in stages.
Business Email Compromise and the Call-Back Rule
Fake vendor invoices and payroll direct-deposit changes work because they look routine. A call-back rule and a few inbox alerts make them harder to pull off, and co-managed IT decides who watches for the warning signs.
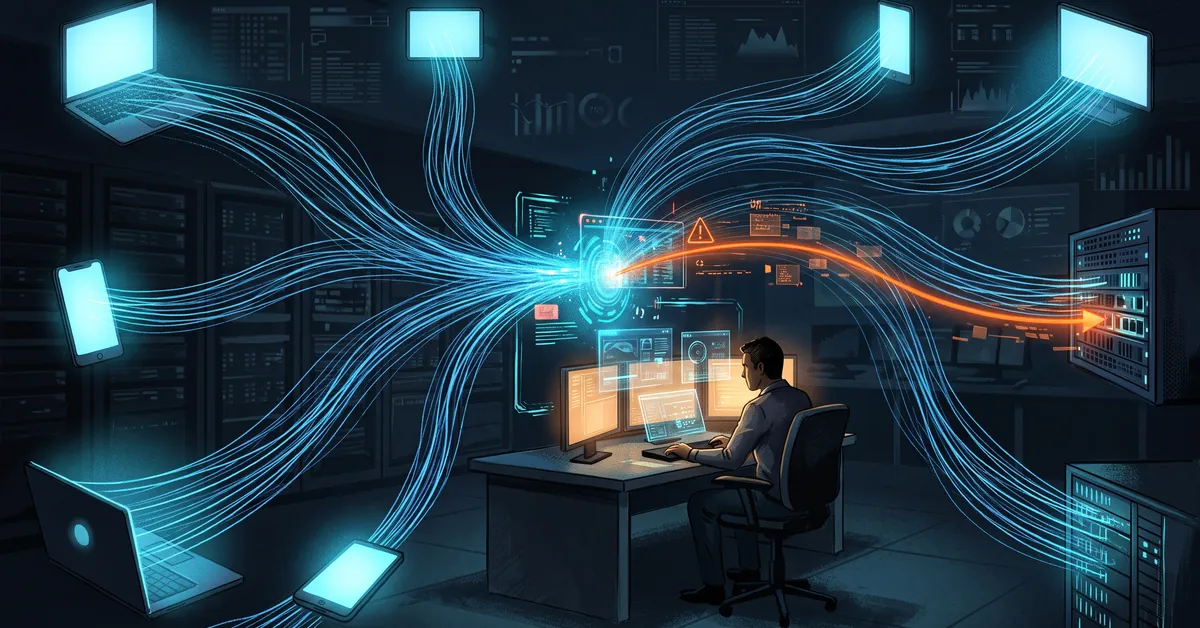
SIEM, SOC, and MDR: Sorting Out Security Acronyms for Small Teams
SIEM is software, a SOC is a team, and MDR is a service. This post explains each in plain words, which logs a small organization should collect, and how co-managed IT splits log ownership from log watching.